CYBERISK SIEM
In development — Pilot program openA security information and event management (SIEM) platform built in-house by CYBERISK LLC. It centralizes security events, correlates them with detection rules, and helps your team triage alerts and measure detection quality. The platform currently runs with an integrated IDS/IPS simulation engine, and we are opening a pilot program to connect it to real small-business environments.
— End-to-end test on a real virtual network: passed
We validated CYBERISK SIEM in a virtual lab of two machines: an Ubuntu 22.04 server as the target (SSH, nginx web server, UFW firewall) and a Kali Linux machine as the attacker. The SIEM ran on the macOS host and received the target's real logs over syslog, with the simulator turned off: 100% real traffic.
- SSH brute-force attack (Hydra) from Kali: detected and correlated as brute force, with the attacker's real IP address
- Port scan (Nmap): firewall blocks detected and classified as a port scan
- SQL injection attempts against the web server: detected in the nginx logs
- Executive security report exported to PDF
Next step: connecting the SIEM to real small-business networks through our pilot program.
- Real-time SOC dashboard: event volume, active and critical alerts
- Live event stream with search and filters by type and severity
- Alert triage workflow: new, acknowledged, in progress, resolved, false positive
- Configurable correlation rules (brute force, port scan, SQL injection, malware beaconing, data exfiltration, DDoS) with severity, sensitivity, and IPS blocking
- Detection quality metrics: precision, recall, F1 score, and confusion matrix
- Executive security reports with CSV and PDF export
Pilot participants help shape the platform before its commercial release.
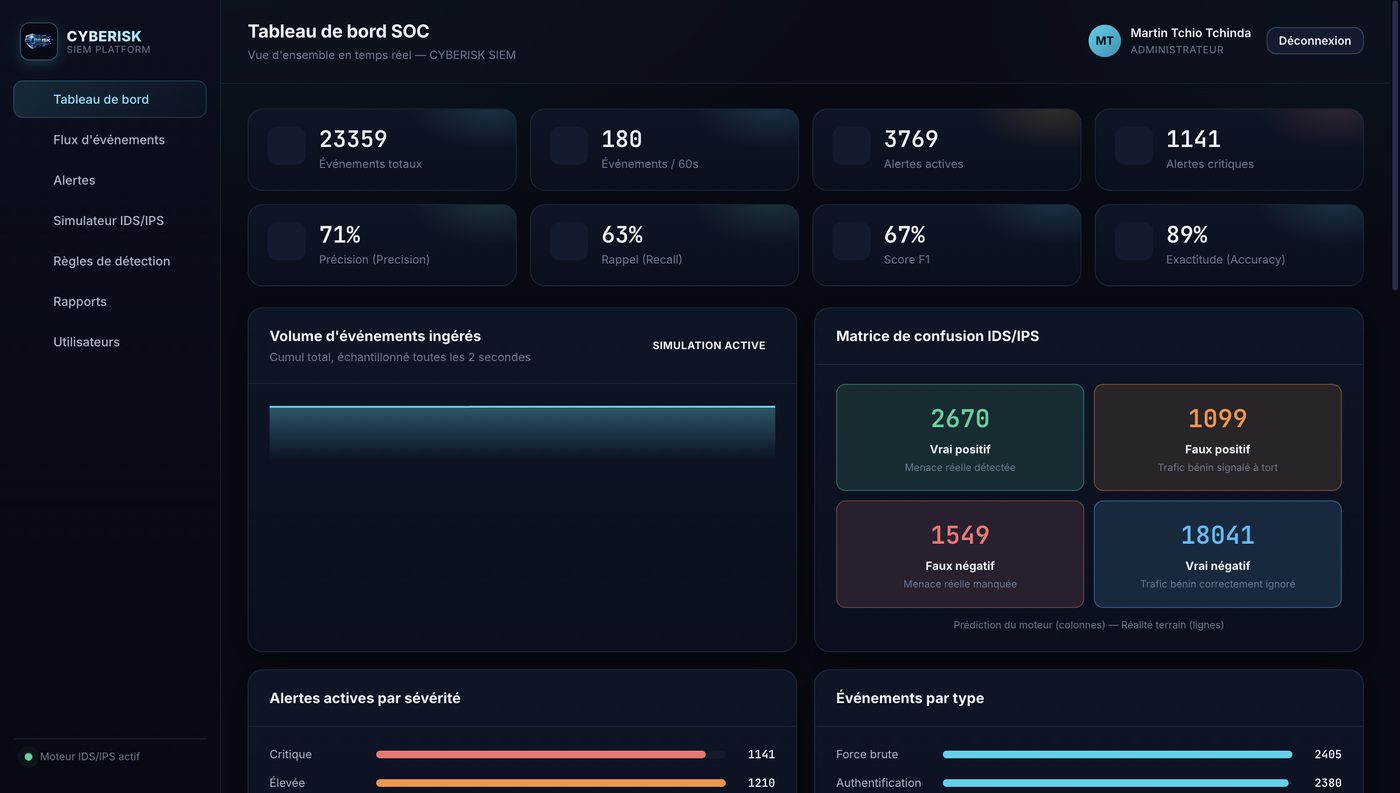
SOC dashboard — real-time overview
A small business without an in-house security team joins the pilot: CYBERISK connects the SIEM to its firewall and server logs, tunes the detection rules to its environment, and delivers a clear monthly security report.