of breaches at small and mid-sized businesses involved ransomware.
Verizon 2025 DBIRCybersecurity and compliance for regulated small businesses
Risk analyses, written security programs and penetration tests for medical and dental practices, CPA firms, auto dealers, insurance agencies and any small business that handles sensitive data.
Based near Chicago. On site across Illinois, remote across the U.S.
Assessments starting at $495. See our pricing →
10:42:07
RULE
HIPAA — risk analysis must be documented
10:42:11
FINDING
RDP port 3389 open to the internet — critical
10:42:16
DEADLINE
IL insurance — notify the DOI within 3 business days
10:42:21
RULE
Auto dealers — penetration test every 12 months
10:42:26
FIXED
MFA enforced on all admin accounts
Registered Vendor — Illinois Procurement Gateway (IPG)
PhD in Computer Science
HIPAA Business Associate Agreement Available
Small offices are the easy target
median ransom paid, before downtime, recovery, and lost clients.
Verizon 2025 DBIRper HIPAA settlement in four ransomware cases OCR resolved in April 2026, all citing an inadequate risk analysis.
HHS OCR, April 2026After a breach, the clock starts at discovery
- 3 business days Illinois insurance regulator
- 30 days FTC, 500+ customers affected
- 60 days HIPAA notice to patients
Which rules apply to your office?
Pick your industry to see the requirement, the deadline and what we deliver.
- The rule
- HIPAA Security Rule
- What it requires
- A documented security risk analysis, kept up to date.
- What we do
- We run the analysis, fix the gaps and help you prepare for ransomware.
- The rule
- FTC Safeguards Rule and IRS Publication 4557
- What it requires
- A written information security program (WISP).
- What we do
- We assess your security, write or review your WISP and test your systems.
- The rule
- FTC Safeguards Rule
- What it requires
- A penetration test every year and a vulnerability assessment every six months.
- What we do
- We deliver both, with a report ready for your compliance file.
- The rule
- Illinois Insurance Data Security Law
- What it requires
- Investigate cybersecurity events and notify the Director within 3 business days. Agencies with 50 or more employees also need a written program.
- What we do
- We tell you what applies and put it in place.
- The rule
- Your clients, your cyber insurer and state breach laws
- What it requires
- Insurers and larger clients now ask for multi-factor authentication, tested backups and a recent security assessment.
- What we do
- A penetration test or cloud security review, and a plain-language action plan you can show them.
- Law firms
- Home care agencies
- Nonprofits
- Real estate offices
- Retail and e-commerce
- Manufacturers
- Schools and daycares
- Public institutions
How it works
-
Free 20-minute call
We identify the rules that apply to you.
-
Assessment
Fixed scope and price, agreed before any work starts.
-
Report and action plan
Plain-language findings and prioritized fixes for your compliance file.
Not sure where you stand?
Answer five yes-or-no questions and get your score and your top gaps.
CYBERISK didn't just launch our website https://apexcaregiver.com — they made sure it was secure from day one. Dr. Tchio Tchinda's team handled everything, from the domain and SSL to protecting our contact forms, and walked us through a clear cybersecurity audit of our operations. As a home care agency handling sensitive client information, that peace of mind matters.
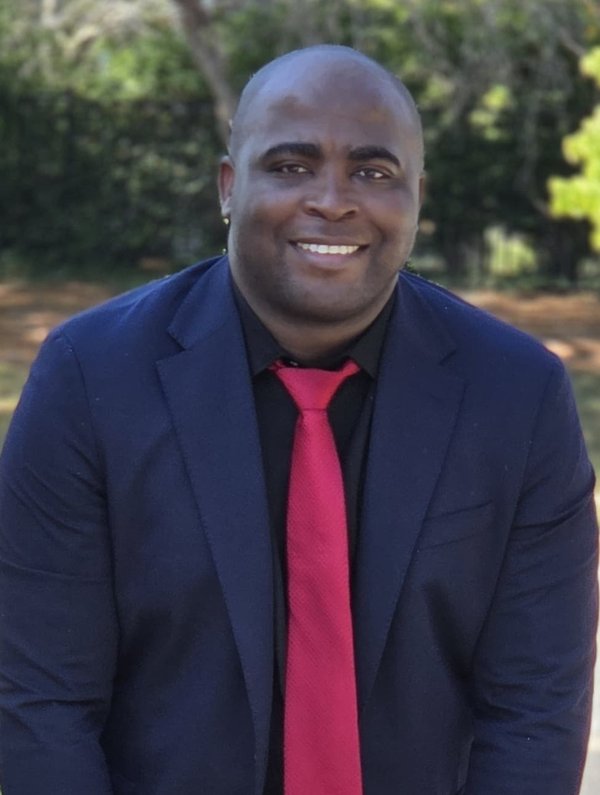
Dr. Martin Guillaume Tchio Tchinda
Founder and CEO of CYBERISK LLC. You work directly with me, from the first call to the final report, and I explain every finding in plain language.
- PhD in Computer Science, research in post-quantum cryptography and cloud security
- M.S. in Cybersecurity Management, Lindenwood University
- Every engagement under a confidentiality agreement, with a signed BAA for healthcare clients
- Registered vendor, Illinois Procurement Gateway (IPG)
Frequently Asked Questions
Answers to the questions practice owners and office managers ask us most.
How does an assessment with CYBERISK work?
It starts with a free 20-minute call to understand your priorities and the rules that apply to you. We then run the agreed assessment and deliver a plain-language report with a prioritized action plan. Book your free call.
How much does it cost?
Every engagement is scoped during the free call. You receive a fixed-price quote before any work starts, so there are no surprises on the invoice.
Will you sign a Business Associate Agreement (BAA)?
Yes. For healthcare clients, we sign a HIPAA Business Associate Agreement before any work that could involve protected health information.
Do you need access to our patient or client records?
In most assessments, no. We test your systems and their configuration, not the content of your records. When access to sensitive data cannot be avoided, it is covered by a confidentiality agreement (and a BAA for healthcare clients) and limited to what the work requires.
Will the assessment disrupt my office?
Testing is scheduled with you in advance, can take place outside business hours, and uses controlled techniques designed to avoid interrupting your daily operations.
Do you only work in Illinois?
No. We are based in Carol Stream, near Chicago, and work on site across Illinois. Risk analyses, written security programs, vulnerability scans and external penetration tests are delivered remotely anywhere in the United States.